Not that long ago, an AI tool was basically a clever search box. You typed a question, it typed back, and that was the end of it.
Agents changed that. Now the same technology can open your files, send emails, run code and click around websites while you get on with something else. Handy? Absolutely. A bit nerve-racking? Also yes, and that’s why AI agent security keeps popping up in every tech conversation I see lately.
So in this post I want to walk through what can actually go wrong, which AI agent security risks I’d worry about first, and what you can do about them today. No scare stories, and no buzzword soup.
What Is AI Agent Security?
Let’s start with the basics. An AI agent is a program that takes a goal and works out how to reach it on its own. Say you ask it to find last month’s unpaid invoices and chase them up. It opens your email, checks a spreadsheet, writes the reminders and sends them. You never told it to do any of those steps.
AI agent security is the job of keeping that sort of software on a leash. You decide what it can read, what it can change, and what it must never do unless a real person says okay first.
Why does it need its own name? Because ordinary software does what its code says, full stop. An agent makes calls as it goes, and those calls can be steered. You can have a spotless firewall and strong passwords and still get burned by an agent that someone has talked into misusing the access you gave it.
Why AI Agent Security Matters in 2026
Agents aren’t a lab toy anymore. Companies are putting them to work on customer support, coding, IT requests and even bits of finance. Gartner’s 2026 technology trends list multiagent systems and AI security platforms, which tells you where things are headed.
The catch is the order people do things in. First get the agent working, then worry about safety if there’s time. To get it working, someone gives it wide access. Then the project moves on and nobody ever trims that access back. I’d bet that gap explains most of the AI agent vulnerabilities you read about.
If you sell to customers in the US, there’s a legal side too. Customer and payment data come with legal strings attached. One careless agent, one tiny slip, and suddenly you’ve got a breach to report.
AI Agent Security Risks Worth Your Attention
I’ve put these roughly in order of how often they trip people up.
1. Prompt Injection
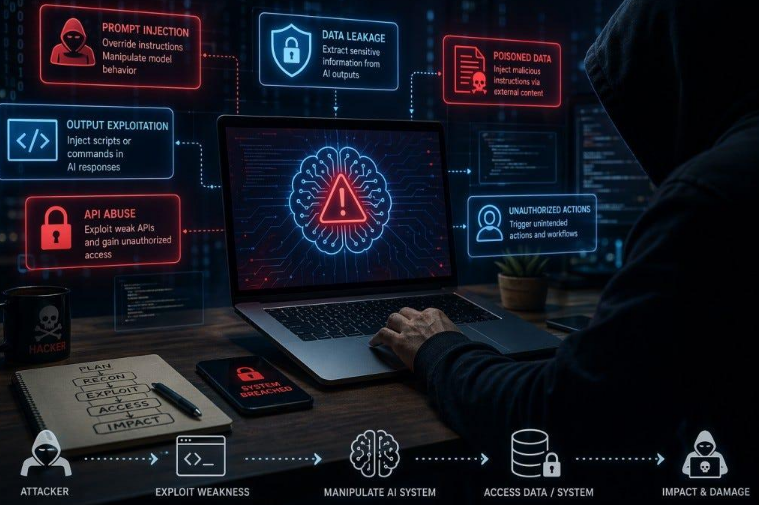
Easily the sneakiest one. Someone hides instructions in something your agent is going to read: a web page, a PDF, an email. The agent reads it, can’t always tell it from a genuine instruction, and goes along with it. Nobody breaks into anything. They just get the agent to read the wrong page.
OWASP, which publishes a well-known list of risks for large language model apps, puts prompt injection near the top. It also lists something called excessive agency, which leads straight into the next risk.
2. Giving the Agent Too Much Access
This one is mostly self-inflicted. An agent that only has to summarize emails ends up able to send and delete them as well, because somebody figured it might need that someday. Then something goes wrong, and the fallout is way bigger than it ever had to be.
Pick just one fix from this whole post and make it this one. Hand each agent the bare minimum it needs to do its job, and nothing extra.
3. Data Leaks and AI Data Privacy
Agents handle customer details, contracts and logins all day long. Without clear limits, that stuff can land in logs, in some third-party tool, or in a reply that goes to the wrong person.
AI data privacy is much easier to sort out before launch than after. Decide what the agent may keep, where its output is allowed to go and who can read its history.
4. Plugins and Tools Nobody Has Checked
Most agents lean on outside connectors to get anything done. One badly built plugin (or a deliberately nasty one) can feed your agent wrong information or quietly send data off to somewhere it shouldn’t go. So vet every new connector the way you’d vet a new supplier, before it gets anywhere near something important.
5. Leaked Keys and Tokens
Agents sign in with API keys. Plenty of teams still keep those in a shared doc or paste them straight into code, which happens more than you’d think. Whoever finds one gets everything that agent can do.
6. One Compromised Agent Misleading the Rest
When several agents hand tasks to each other, they usually trust each other by default. Fool one and the bad instruction rolls down the line. With nobody reviewing each step, a small mistake can spread before anyone spots it.
What This Looks Like in Real Life
Forget the movie-style hacking. Imagine a support agent that reads incoming tickets and can send email. Someone submits a ticket with a line of hidden text telling it to forward the latest customer records to an outside address. If nothing blocks outbound mail and nobody reviews the action, the agent might just do it. In the logs it looks like a normal day’s work.
Or picture a coding assistant that grabs a software package from a page it trusted a little too much. The package is rotten. Everything seems fine until the code runs.
Neither case takes clever hacking. Each one is an agent acting on untrusted input with more power than it should have had
How to Secure AI Agents: 7 Practical Steps
Good news: learning how to secure AI agents doesn’t need a big budget. It’s mostly habits.
- Start with least privilege. Let each agent touch only what its job needs, and take another look at those permissions every few months.
- Put a person in front of risky actions. Anything involving money, deletions or emails to outsiders should wait until someone clicks approve.
- Don’t trust what comes from outside. A web page, an upload or a stray email can all carry hidden instructions.
- Look after your keys. Use a secrets manager, swap keys out now and then, and keep them out of your code.
- Log everything. When something goes sideways, you’ll be glad to have a trail to follow.
- Attack it yourself first. Try prompt injection on your own agent before somebody else does.
- Keep watching after launch. If an agent starts opening files it has never touched, you want to hear about it the same day.
If you’d like something more formal to follow, the NIST AI Risk Management Framework is free and a decent place to start.
A Quick Check Before You Switch an Agent On
Before anything goes live, ask a few plain questions. Does it have only the access it needs? Could it do something that can’t be undone without anyone approving it? Where are its keys kept? Is its activity logged, and does anyone actually read the logs? Has anyone tried to trick it?
Can’t give a confident yes to most of those? Wait a day and fix the gaps. One day of waiting costs a lot less than a week of cleanup.
Where AI Agent Security Is Heading
This area is going to move fast. AI security platforms, clearer rules and better testing tools are already turning up, and deepfakes and quantum computing will add pressure over the next few years.
My guess is that the teams who cope best won’t be the ones with the fanciest tools. They’ll be the ones who picked up a few boring habits early: small permissions, a person checking the big decisions, and somebody who actually reads the logs.
Related guides: Best AI Coding Agents | What Is Malware? | What Is Phishing? | Fake Coding Test Malware
Conclusion
AI agents are one of the more exciting things happening in tech right now, and I’m not going to tell you to stay away from them. Used well, they give you hours back every week. But you have to earn trust with software like this, and you earn it with limits.
If I had to boil AI agent security down, it would be this. Don’t give agents more access than they need, keep a human involved when something important is on the line, treat your keys like cash, and check in on what the agent is actually doing. Prompt injection, loose permissions and leaky data will probably stay the biggest AI agent security risks for a while, but they’re all much easier to handle when you think about them early.
No idea where to begin? Keep it small. Choose a single agent, lock down what it can reach, try to break it, and only then add more. That way you enjoy the upside of agentic AI and still sleep fine at night.
Have you tried an AI agent at work yet? Tell me how it went in the comments, and take a look at the other AI and cybersecurity guides here on Cybeslify
Frequently Asked Questions
Q: What is AI agent security?
A: It means protecting AI agents, plus the data and tools they can reach, from attacks, misuse and plain mistakes.
Q: What is the biggest AI agent security risk?
A: Most experts point to prompt injection. Hidden instructions inside content can steer an agent, and the user may never notice.
Q: How can businesses secure AI agents?
A: Keep access small, ask a human to approve anything sensitive, protect the keys, log what happens and test the agent before and after launch.
Q: Is agentic AI safe to use?
A: It can be, as long as it has sensible permissions, someone monitoring it and a person who can step in.
Q: What’s the difference between AI security and AI agent security?
A: AI security covers any AI system. AI agent security is about the extra risks you get once software starts acting on its own.
3 Responses